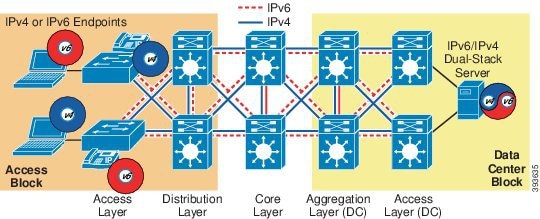
Deploying Enterprise Network Protocols within Corporate Environments
the on-ramp is almost frictionless and the platform reaches complete SSE safe web entrance, CASB, and web browser isolation without changing vendors. deep legacy-application assistance and complex AD-centric attribution take more work than the standard VPN incumbents. companies wanting to retire VPN devices and embrace no trust progressively. totally free tier; released per-user plans; business by quote. quote-based, tiered licensing. [VALIDATE: current SKU structure] Cisco Secure Client AnyConnect VPN connection and posture status Palo Alto GlobalProtect remote gain access to entrance policy configuration remote access with the full NGFW assessment stack applied to the tunnel App-ID, risk avoidance, and URL filtering imposed on remote traffic. inspection depth. Traffic through GlobalProtect gets the very same analysis as traffic through your PA firewall softwares, with Prisma Gain access to extending it to ZTNA 2.0.
companies currently running Palo Alto next-generation firewalls. quote-based (licensed with PA platform/Prisma Gain access to). Palo Alto GlobalProtect remote gain access to gateway policy configuration Fortinet FortiClient VPN and FortiSASE remote gain access to dashboard FortiClient VPN is included with FortiGate firewall softwares, making it the default remote-access method for an enormous installed base and FortiSASE extends it toward ZTNA. If you own FortiGates, capable remote access is successfully already spent for, with ZTNA readily available as you update. Fortinet's exploited-vulnerability history (consisting of a FortiCloud authentication bypass included to CISA's KEV brochure in January 2026) makes disciplined patching compulsory for internet-facing entrances. the lots of companies currently running Fortinet at the edge.
Fortinet FortiClient VPN and FortiSASE remote gain access to dashboard NordLayer organization VPN group management and gateway configuration NordLayer offers business-grade network security with transparent prices, operating on a cloud-based Zero Trust architecture and devoted IP facilities designed for distributed groups. quickly setup, dedicated IP alternatives, device posture checks, and per-user prices you can budget without a sales call.
Managing the Shift to Enterprise IPV6 Networkssmall and mid-sized companies wanting quick, manageable secure access. published per-user monthly tiers. [VALIDATE: existing rates] NordLayer service VPN group management and entrance setup Inspect Point Harmony SASE secure network access management console Border 81's cloud-native architecture obtained by Examine Point is provided as Harmony SASE, combining ease of use with Check Point risk avoidance.
Evaluating the Impact of Cloud Proxy Services
transparent per-user tiers plus enterprise-grade security research behind the platform, bridging the SMB/enterprise gap. product packaging has evolved significantly post-acquisition; validate current tier limits and feature mapping before finalizing. SMBs and mid-market teams desiring ZTNA with a security supplier's support. published per-user tiers. [CONFIRM: existing Consistency SASE packaging] Check Point Consistency SASE safe and secure network access management console OpenVPN Gain access to Server administration and connection management The open-source standard for secure connection, offered as self-hosted software application (Neighborhood/ Access Server) or CloudConnexa.
you can run it totally yourself, examine the code, and pay nothing but facilities truly important for technical groups and constrained spending plans. self-hosting ways you own patching, accessibility, and scaling; efficiency tuning is your problem; support is community-based unless you buy industrial editions. technical teams, cost-sensitive companies, and anyone needing full control.
[VALIDATE: present prices] OpenVPN Gain access to Server administration and connection management Zscaler Private Gain access to no trust application access dashboard Zscaler Private Access (ZPA) brokers protected connections through a global cloud architecture, making sure applications are never ever exposed to the public web. IT teams maintain representative health using the Zscaler Customer Connector and Zero Trust Exchange.
Top Cloud Security Best Practices for 2026
Zscaler Private Gain access to zero trust application access dashboard TwingateZTNAYesYesVPN replacementHoursTailscaleMesh (WireGuard)YesYesEngineering teamsHoursCloudflareZTNA/SSEYesYesProgressive zero trustHoursdaysCisco Secure ClientVPN + ZTNANoNoCisco enterprisesWeeksPalo Alto GlobalProtectVPN + ZTNA 2.0 NoNoPA estatesWeeksFortinetVPN + SASEBundledPartialFortiGate estatesDaysNordLayerVPN/ZTNA hybridTrialYesSMBsHoursCheck Point Harmony SASEZTNA/SASETrialYesSMBmid-marketHoursdaysOpenVPNSelf-hosted/cloudCommunityPartialTechnical teamsDaysweeksZscalerZTNA (SSE)NoNoLarge enterpriseWeeksmonths 5 checks separate a great decision from an expensive one.
Thick customers, SMB shares, and RDP act differently under ZTNA than under a VPN. Cloud-delivered access adds a hop; test from the areas where your individuals really work before dedicating.
Business VPN and safe gain access to pricing divides easily. (Twingate, Tailscale, NordLayer, Harmony SASE, Cloudflare) typically run from a few dollars to low double digits per user each month, with free tiers for little teams budgeting is insignificant and procurement is quick. (Cisco, Palo Alto, Zscaler, Fortinet's SASE tiers) cost per user with volume discounts, and complete SSE packages benchmark around the $15$25 per user monthly variety at list before business discount rates of 3050%.
Standard VPNs remain useful for full-network administrative gain access to, legacy procedures, and site-to-site connection. Due to the fact that they are internet-facing by style and sit at a relied on point in the network. Remote-access products from multiple significant vendors have appeared consistently in CISA's Understood Exploited Vulnerabilities catalog, making patch speed and decreased network direct exposure the 2 crucial defensive steps.
Implementing Next-Gen VPN Protocols for Corporate Environments
Twingate, Tailscale, and Cloudflare provide genuine totally free tiers suitable for little groups, and OpenVPN is genuinely open source. Prevent consumer "totally free VPN" services for business use they're constructed for personal privacy browsing, not business access control, and frequently do not have audit logging and device policy.
A customer VPN paths personal traffic through a service provider's servers for privacy. If your VPN is slow, over-permissioned, and overdue for replacement, begin with Twingate or Tailscale if your team lives in the terminal.
Other VPNs leave you to translate and carry out Zero Trust on your own. Proton gives you a simple approach that lets you define gain access to by group, impose it immediately, and prevent policy sprawl.
Strategic IPv6 Migration Tactics to Scalability
Nowadays, keeping your business safe needs a lot more than running an anti-virus program once in a while and wishing the very best. Among the most essential tools your business can use is a Virtual Private Network, or VPN. A business VPN is more than simply geo-blocking, it's an absolute requirement for service these days.
Managing the Shift to Enterprise IPV6 Networks
An organization VPN needs to: Supply safe and secure access to business resources and cloud services by workers and organization partners; Secure delicate details accessed from out of the workplace; Protect versus information collection by ISPs and even foreign governments; Supply account management, central billing, and malware protection; Filter material such as streaming or social networks, whether for time management or security; and Do it all quickly and effectively.